The FS AI RMF Release and Strategic Context
On 19 February 2026, the US Department of the Treasury released the Financial Services AI Risk Management Framework (FS AI RMF) alongside an AI Lexicon. Developed through public-private collaboration, the framework adapts NIST AI RMF to financial-services risk management. CRI's version 1.0 contains 230 control objectives for institutions to tailor to their AI adoption stage and risk context. Treasury release; CRI framework resources.
Treasury's release does not establish the framework as a statutory requirement or announce an examination-manual adoption deadline. CRI describes adaptable, non-prescriptive control objectives that complement existing governance and risk programmes. Move78 recommends using the relevant objectives to review controls, owners and evidence alongside applicable legal duties and current guidance from your institution's supervisor.
CRI provides an AI Adoption Stage Questionnaire, a Risk and Control Matrix with 230 control objectives, a Guidebook and a Control Objective Reference Guide. The questionnaire and matrix support stage-specific selection; the reference guide supplies illustrative controls and evidence to adapt to the institution's context.
For financial-services SMEs, the framework can help prioritise sector-specific control gaps and organise evidence for discussions with bank partners. Check the partner's actual due-diligence requirements and the current guidance from the relevant supervisor; the framework's release and objective count do not establish a universal compliance baseline.
Already implementing NIST AI RMF? The FS AI RMF is designed as an overlay, not a replacement. You extend your existing GOVERN, MAP, MEASURE, MANAGE implementation with sector-specific controls rather than starting from scratch.
See our NIST AI RMF implementation guide for the base framework.
Singapore financial-institution update: MAS guidance
MAS issued final AI risk-management guidelines on 7 October 2026 for financial institutions under its supervision, covering AI use including generative and agentic AI. Implementation is proportionate to the institution's activities and risk exposure. Existing governance structures may provide oversight where accountability and coordination are adequate; a dedicated AI committee is not universally required.
The phased dates are 7 October 2027 for oversight and key risk-management systems, policies and procedures (Sections 3–4), and 7 October 2028 for life-cycle controls and capability/capacity (Sections 5–6). Institutions meeting the low-material-impact criteria in paragraph 2.3 may use basic governance policies and procedures. The consultation response says appropriate life-cycle controls for high-risk use cases should be applied as soon as possible. These are Singapore supervisory expectations, separate from the US FS AI RMF and IMDA's national frameworks.
Source review for this update: 9 October 2026. Scope: FS AI RMF release/status and the MAS 7 October 2026 guidelines. Source basis: MAS final guidelines (paragraphs 1.1–1.8, 2.1–2.5 and 3.3), consultation response (paragraphs 5.3 and 13.5–13.6), and official release.
The 230 Control Objectives — What They Cover
CRI's official structure follows the NIST AI RMF GOVERN, MAP, MEASURE and MANAGE functions, categories and subcategories, with 230 additional control objectives. The five sections below are Move78 review themes, not five official CRI categories. Use CRI's original matrix for objective identifiers and stage applicability.
Model Risk Management
Move78 review theme: record model purpose, validation, monitoring, limitations and accountable owners. For U.S. banking organisations, SR 26-2, issued on 17 April 2026, replaced SR 11-7. The revised guidance is risk-based and non-prescriptive, generally most relevant to banks above $30 billion in assets, with possible relevance to smaller banks with significant model risk. Its principles cover traditional quantitative models and non-generative, non-agentic AI models; generative and agentic AI are outside its scope. Review the actual guidance and OCC Bulletin 2026-13 before applying it. Suggested records include model inventories, validation reports, monitoring results and governance decisions.
Data Integrity and Quality
Move78 review theme: inspect data quality, provenance, representativeness and retention for the intended use. Test for weaknesses in training and evaluation data rather than assuming that a control label prevents bias or error. Suggested records include data quality scorecards, lineage documentation and evaluation findings.
Explainability and Interpretability
Move78 review theme: document decision drivers, model limitations and the explanation available to an affected customer. Check the applicable legal process for the decision and jurisdiction separately. Suggested records include explanation reports, decision records and reviewed customer communications. These examples do not extend a credit-law duty to insurance, employment or other decisions.
Bias Detection and Mitigation
Move78 review theme: select fairness tests appropriate to the system, affected population and intended use. Record the methods, results, limitations and mitigation decisions. Obtain qualified review of any applicable discrimination or consumer-protection duties; a framework theme does not establish which law applies. Suggested records include evaluation reports, monitoring metrics and remediation records.
Operational Resilience
Move78 review theme: define fallback arrangements, human intervention, incident handling and continuity for AI-dependent workflows. Suggested records include incident plans, override logs, continuity exercises and failover tests. Test these arrangements in the deployment context.
Move78 recommendation: monitor degraded performance as well as outages. For example, a fraud model may remain available while missing a pattern it previously detected. Define a justified monitoring threshold, an accountable reviewer and a response to deteriorating performance; test the threshold against the system's actual use.
Financial-Services Review Priorities
Use the relevant CRI control objectives to examine sector-specific risks alongside existing NIST AI RMF work. The following are Move78 implementation recommendations, not additional statutory requirements created by the framework.
- Model risk review: Tailor validation and monitoring to model use and materiality, document limitations and assign objective review. Use current supervisory guidance within its actual scope. CRI's framework does not amend U.S. guidance or impose one validation cadence for every AI system.
- Consumer-impact review: Examine potentially unfair outcomes and document affected people, test methods, results, mitigation decisions and responsible owners. Check the applicable credit, insurance or other consumer law separately before deployment.
- Adversarial testing: Select tests proportionate to the use case and threat model, including manipulation or poisoned-data scenarios where relevant. Record findings and remediation decisions rather than assuming the same test regime applies to every financial model.
- Vendor oversight: Review model methodology, testing, data handling, change management and incident coordination. Seek evidence and contractual terms appropriate to the relationship, available assurance and identified risks.
- Incident notification: Determine duties from the entity, jurisdiction, event and applicable instrument. For U.S. national banks, federal savings associations and federal branches/agencies covered by 12 CFR Part 53, apply its computer-security notification-incident definitions and notification rules; see the OCC final-rule explanation. An AI incident is not automatically a notification incident. The voluntary FS AI RMF itself does not create a blanket AI-reporting duty.
Move78 recommendation: compare current evidence with each relevant CRI objective and record the scope, owner, evidence, gap and next action. Determine coverage from that review rather than assuming a percentage of reuse from generic AI governance or the name of an existing framework.
AI Adoption Stages and Scaling Controls
CRI's version 1.0 AI Adoption Stage Questionnaire uses four stages: Initial, Minimal, Evolving and Embedded. Apply the original questionnaire and its six dimensions to determine the stage; organisation size or a generic maturity label does not substitute for its decision process.
- Initial: Limited, protective approaches to AI use.
- Minimal: Limited, lower-risk implementations.
- Evolving: Broader production use with greater risk exposure.
- Embedded: AI integrated widely across the organisation.
These brief descriptions orient the reader; CRI's questionnaire determines the stage and its matrix identifies the corresponding objectives. CRI adoption-stage descriptions are not legal risk classifications. Choose the applicable objectives and document any additional controls justified by the institution's risks.
Move78's separate financial-services readiness assessment is a 12-question management screen. It does not reproduce CRI's Adoption Stage Questionnaire or assign its four official stages. Keep a management-screen result distinct from the original CRI stage determination.
Move78 recommendation: establish accountable owners, an AI inventory, permitted-use boundaries and evidence priorities that fit the current use. Reassess when the use, data, business impact or deployment changes. Framework staging does not grant permission to deploy or replace applicable legal and supervisory requirements.
FS AI RMF vs NIST AI RMF Comparison
| Dimension | NIST AI RMF 1.0 | Treasury FS AI RMF |
|---|---|---|
| Scope | All AI applications across all sectors | Financial services sector only |
| Framework structure | 4 functions, 19 categories, 72 subcategories | NIST-aligned structure plus 230 control objectives |
| Industry context | Generic; broad stakeholder base | Banking, insurance, payments and other financial services |
| Status | Voluntary risk-management framework | Industry-led implementation framework |
| Implementation guidance | Playbook with suggested actions | Control reference guide + implementation matrix |
| Adoption staging | Profiles (current/target state) | Questionnaire: Initial, Minimal, Evolving, Embedded |
| Risk context | Broad AI trustworthiness risks | Financial-services risk context |
| Implementation use | Risk-management outcomes; not certification | Context-specific controls and evidence; not a universal examination benchmark |
NIST AI RMF 1.0 has four functions, 19 categories and 72 subcategories describing risk-management outcomes and actions. CRI's FS AI RMF adds 230 control objectives and illustrative implementation/evidence guidance for financial services. Use the NIST Core and CRI source documents to identify the outcome and objective relevant to the system; the objective count is not a measure of compliance.
Cross-Framework Evidence Planning: ISO 42001, NIST AI RMF and FS AI RMF
ISO/IEC 42001 provides an AI management-system context; NIST AI RMF provides risk-management outcomes; CRI's FS AI RMF adds sector-specific objectives. An organisation may use them together, but each has its own scope. Verify any ISO requirement or control-level crosswalk against licensed text rather than relying on an assumed Annex A count or clause shorthand.
Move78 recommendation: when reusing evidence, identify the system, owner, purpose, NIST outcome and CRI objective, then verify any relevant ISO requirement from licensed text. Record mapping strength, conditions, exclusions and additional evidence needed. A shared record does not automatically satisfy multiple frameworks.
For example, a credit-model validation report may inform several reviews. Document which question it answers for each review, the tested population, model limitations and any missing evidence. Have the relevant reviewer assess suitability before accepting it. This is an illustrative evidence-planning example, not a verified three-framework equivalence or an automatic consumer-law conclusion.
Colorado SB26-189 replaces the former framework-linked affirmative-defence regime. Combining ISO 42001, NIST AI RMF and sector governance records does not establish current Colorado compliance or satisfy an examiner automatically. Use a separate current-law review. See the Colorado ADMT guide.
Need implementation support? ACT is one editable AI Controls Toolkit with eleven core files across eight workflow areas. It supports evidence collection and human decisions; it does not enforce controls or certify compliance. This guide does not establish exhaustive coverage of all 230 objectives or licensed ISO clauses.
Implementation Timeline for Mid-Size Financial Services Firms
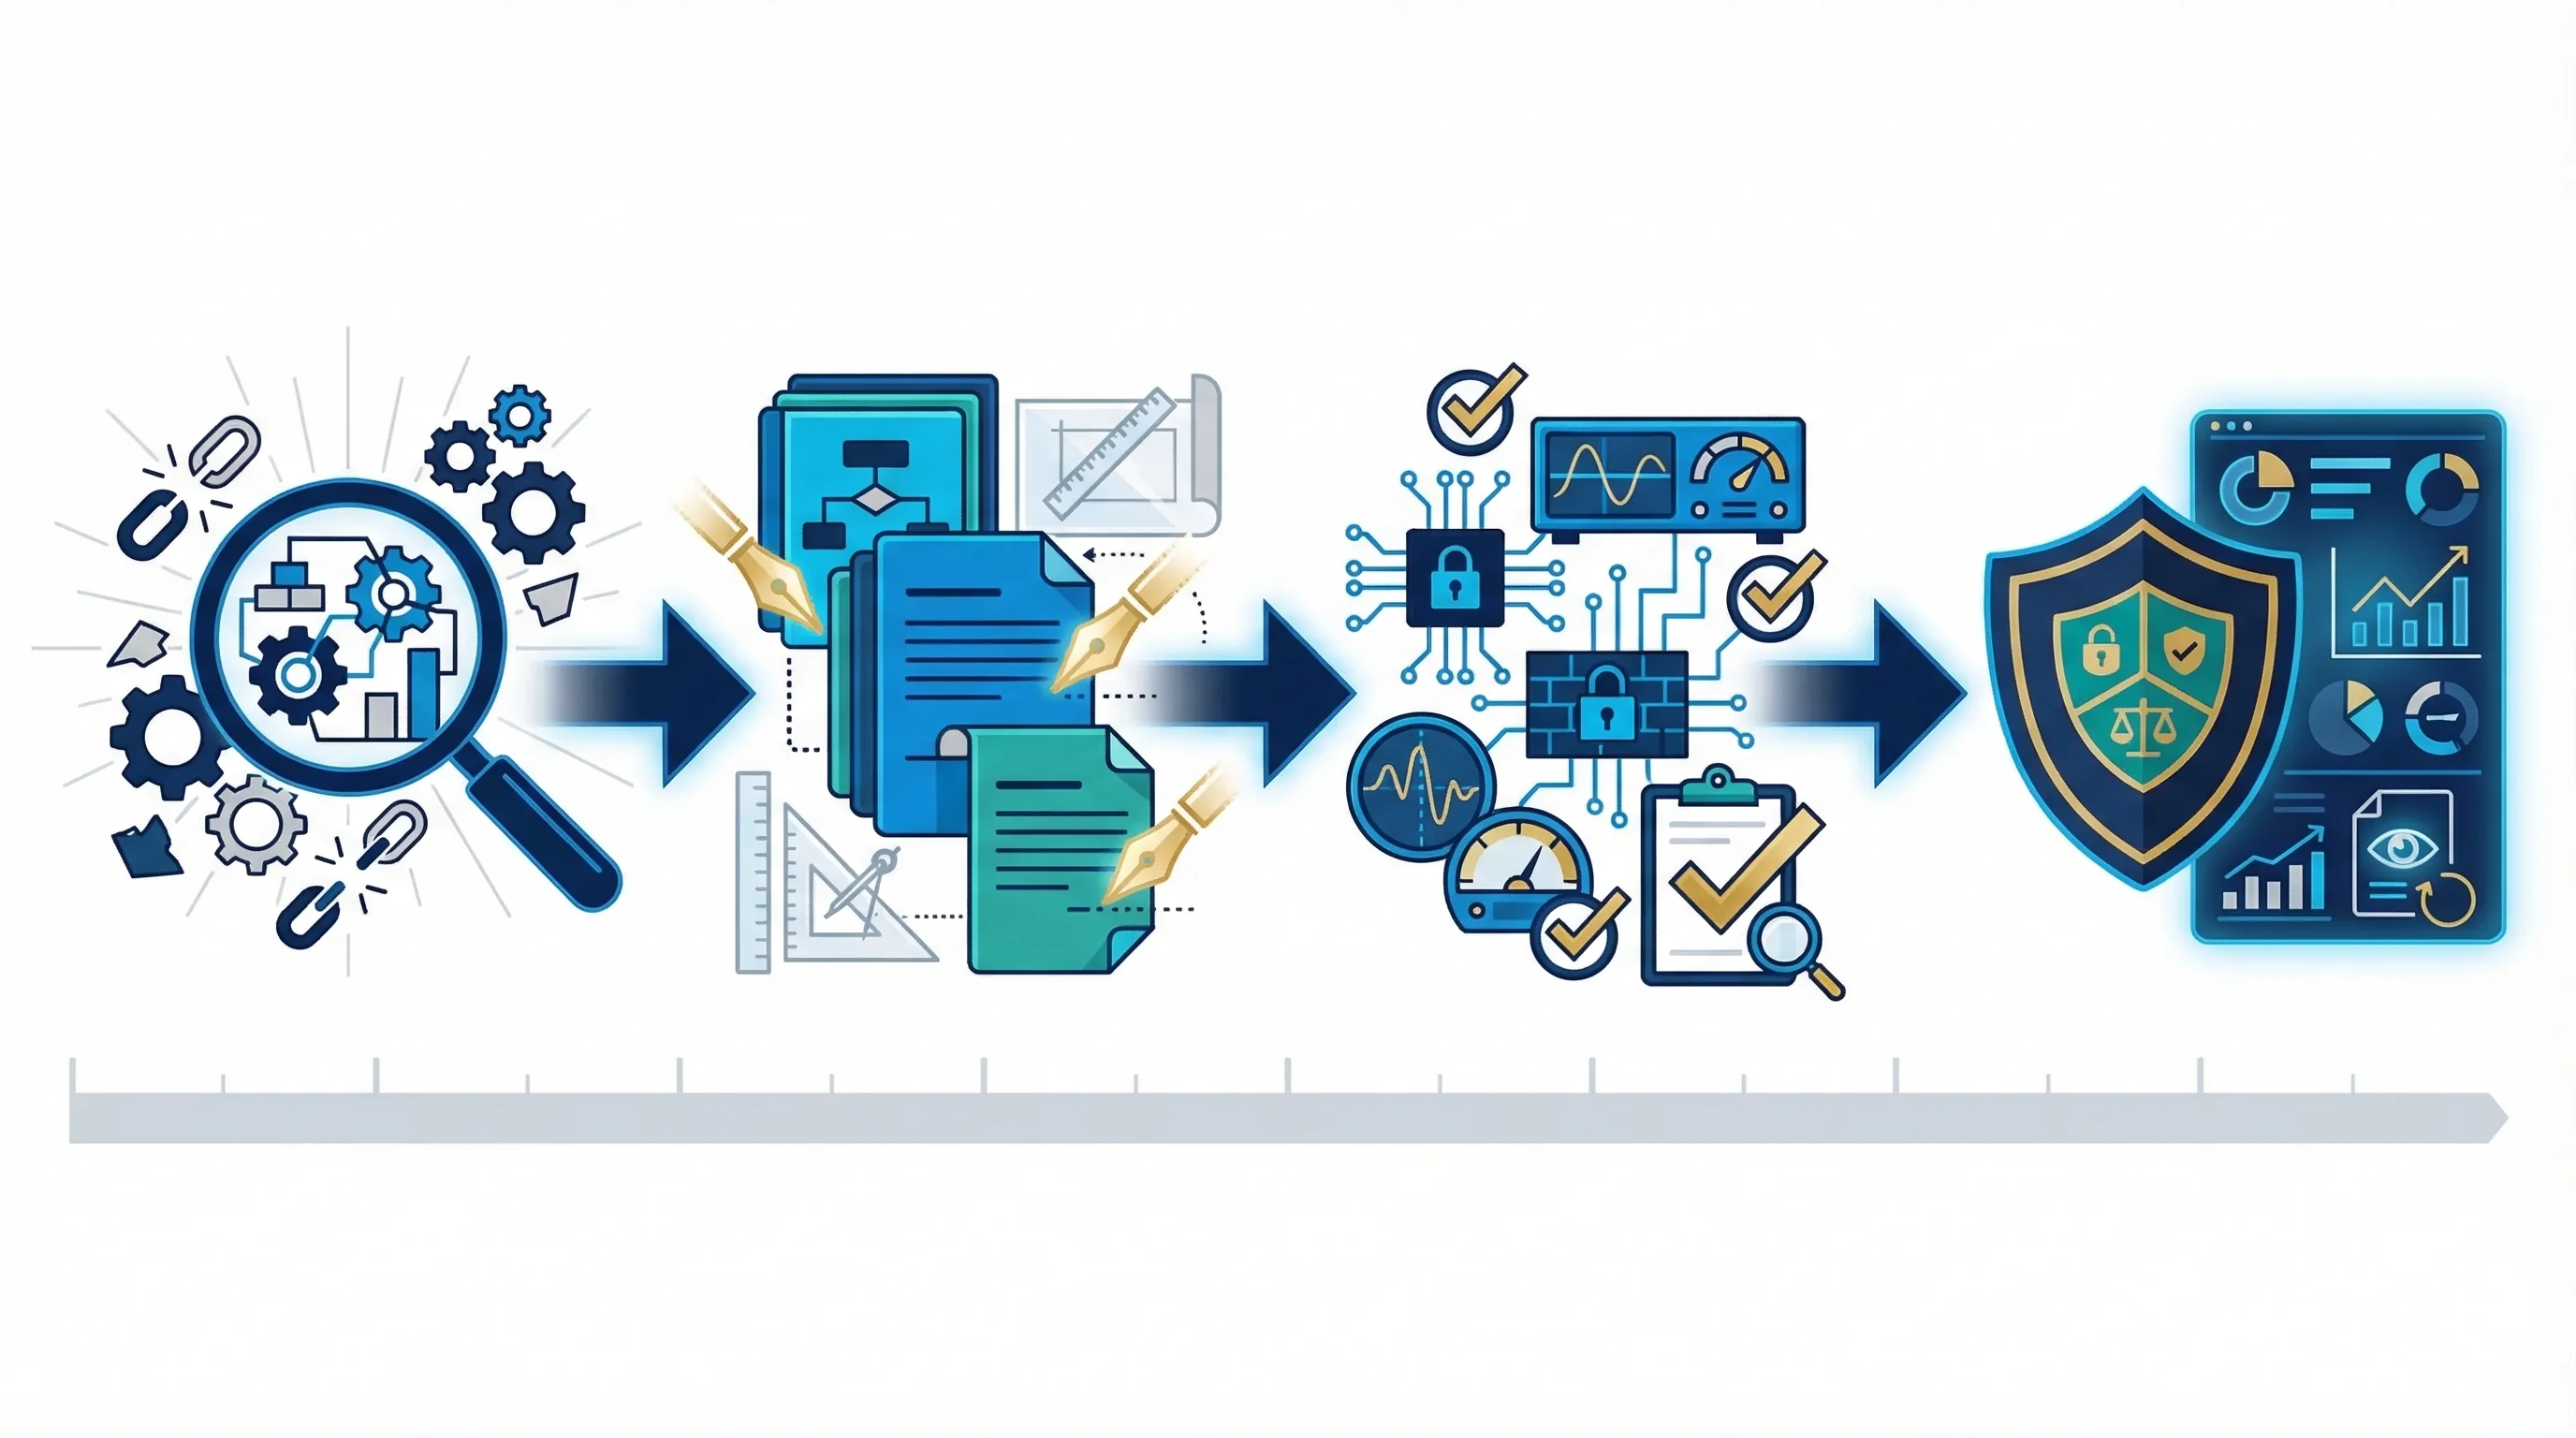
Use the following as a Move78 planning example. Set phase durations from the actual systems, evidence gaps, available reviewers and applicable requirements. The month labels illustrate sequencing; they are not a validated delivery estimate or supervisory timetable.
Months 1–3: Gap Analysis and Foundation. Apply CRI's original questionnaire, identify the relevant objectives and record current evidence and gaps. Organise the control inventory using the source framework's identifiers, with a separate record of any cross-framework mappings that require verification.
Months 4–6: Policy and Priority Controls. In this planning example, establish or update the governance arrangements and address the highest justified risks. Review model/data controls and vendor evidence, with testing and contractual decisions suited to the use case. This is not a prediction of where examiners will look first.
Months 7–9: Implementation and Review. Address the remaining relevant objectives, including explanation, fairness and continuity risks. Check performance and control evidence through an appropriately objective review, record weaknesses and track remediation. Determine any audit requirements separately from this framework example.
Months 10–12: Evidence and Management Review. Review the evidence portfolio with accountable owners, agree realistic retrieval targets and brief management on remaining risks and actions. Prepare for the applicable review process without treating this sequence as an assurance of examination readiness.
Move78 recommendation: brief the board in terms of model risk, customer impact and operational resilience. Show the source-based adoption-stage decision, relevant control objectives, evidence gaps and planned actions. Keep the legal and supervisory applicability decision separate from a framework completion percentage.
Move78 recommendation: maintain versioned controls and evidence, and review the source-owner framework and applicable regulatory publications when material changes occur. CRI's version 1.0 is the basis of this guide; a future update should be assessed on its actual content.
Starting implementation? ACT is one editable AI Controls Toolkit with eleven core files across eight workflow areas. It supports evidence collection and human decisions; it does not enforce controls or certify compliance. Specify the financial-services objectives and evidence records you need.